
IDENTITY AND ACCESS RISK PLATFORM
Know who has access. Understand the risk. Keep decisions accountable.
TPZ is building a clearer way for security teams to manage identity and access risk, from understanding what needs attention to governing the actions taken to resolve it.
Starting with read-only Microsoft Entra investigation. Our Design Partner Beta is designed to validate customer-authorized actions, read-back verification, and retained evidence.
THE GOVERNANCE PROBLEM
Who has access, who decides, and who checks what happened?
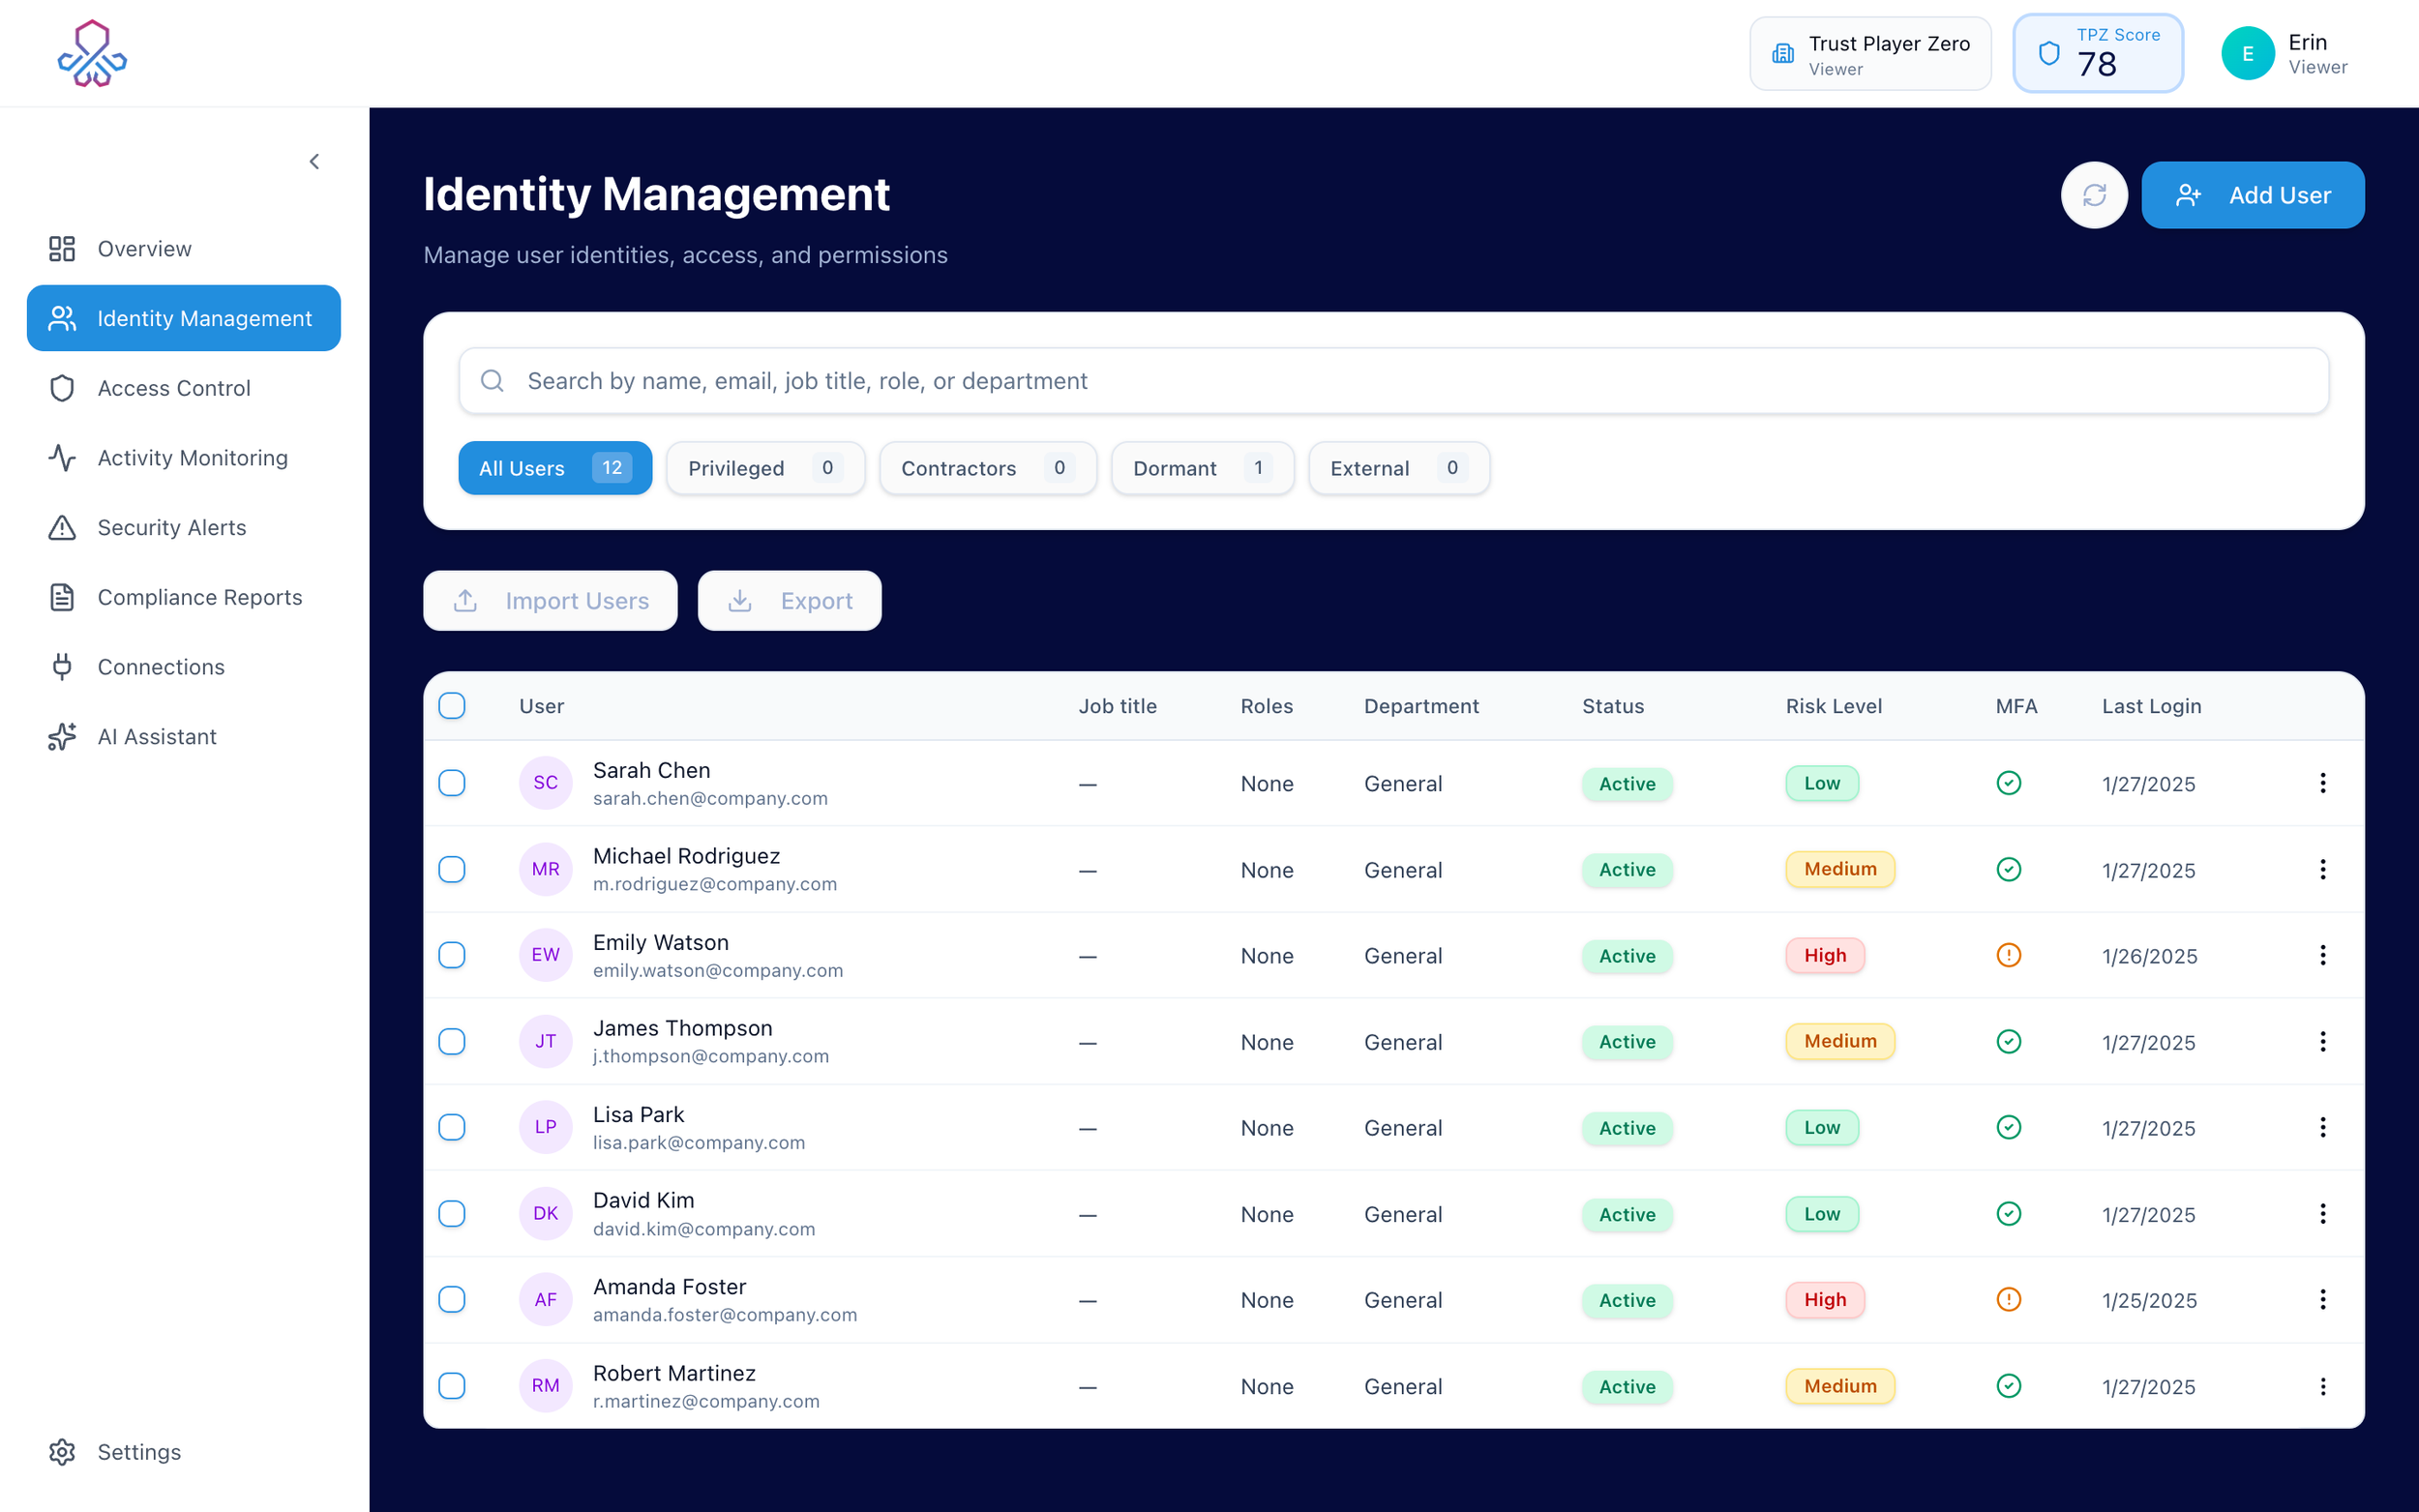
A user can have access in one system, privileged permissions in another, and a pending security review somewhere else. The evidence needed to understand the issue may be spread across dashboards, administrative consoles, and tickets.
For a small security team, the difficult part is often coordinating what happens next. Someone needs to review the evidence, decide whether a change is appropriate, authorize that change, and confirm the result.
Without a clear process, important security decisions can get lost between systems.
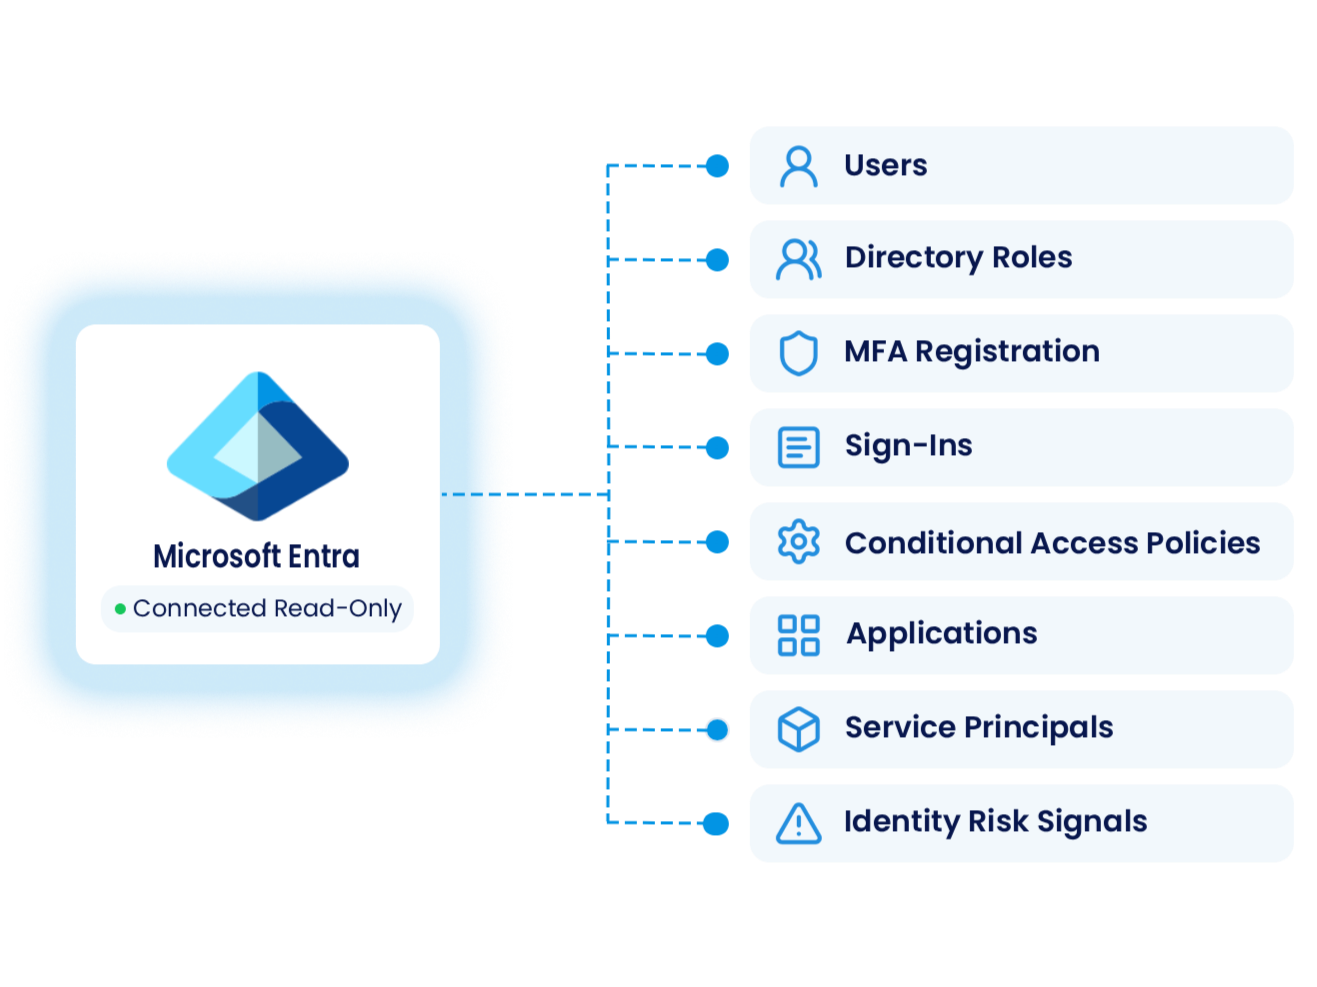
Users
Who they are, where they’re from, and their account status.
Directory Roles
Assigned Microsoft Entra directory roles.
MFA Registration
Registered authentication methods and registration gaps.
Sign-ins
Recent activity, locations, devices, and anomalies.
Access Policies
Conditional Access policies configured in Entra.
Risk Signals
Identity Protection risk context and other supported security signals.
TPZ is designed to complement the systems teams already use by bringing more of that identity and access workflow together.
FROM SIGNALS TO INVESTIGATION
Understand the evidence before deciding what to do.
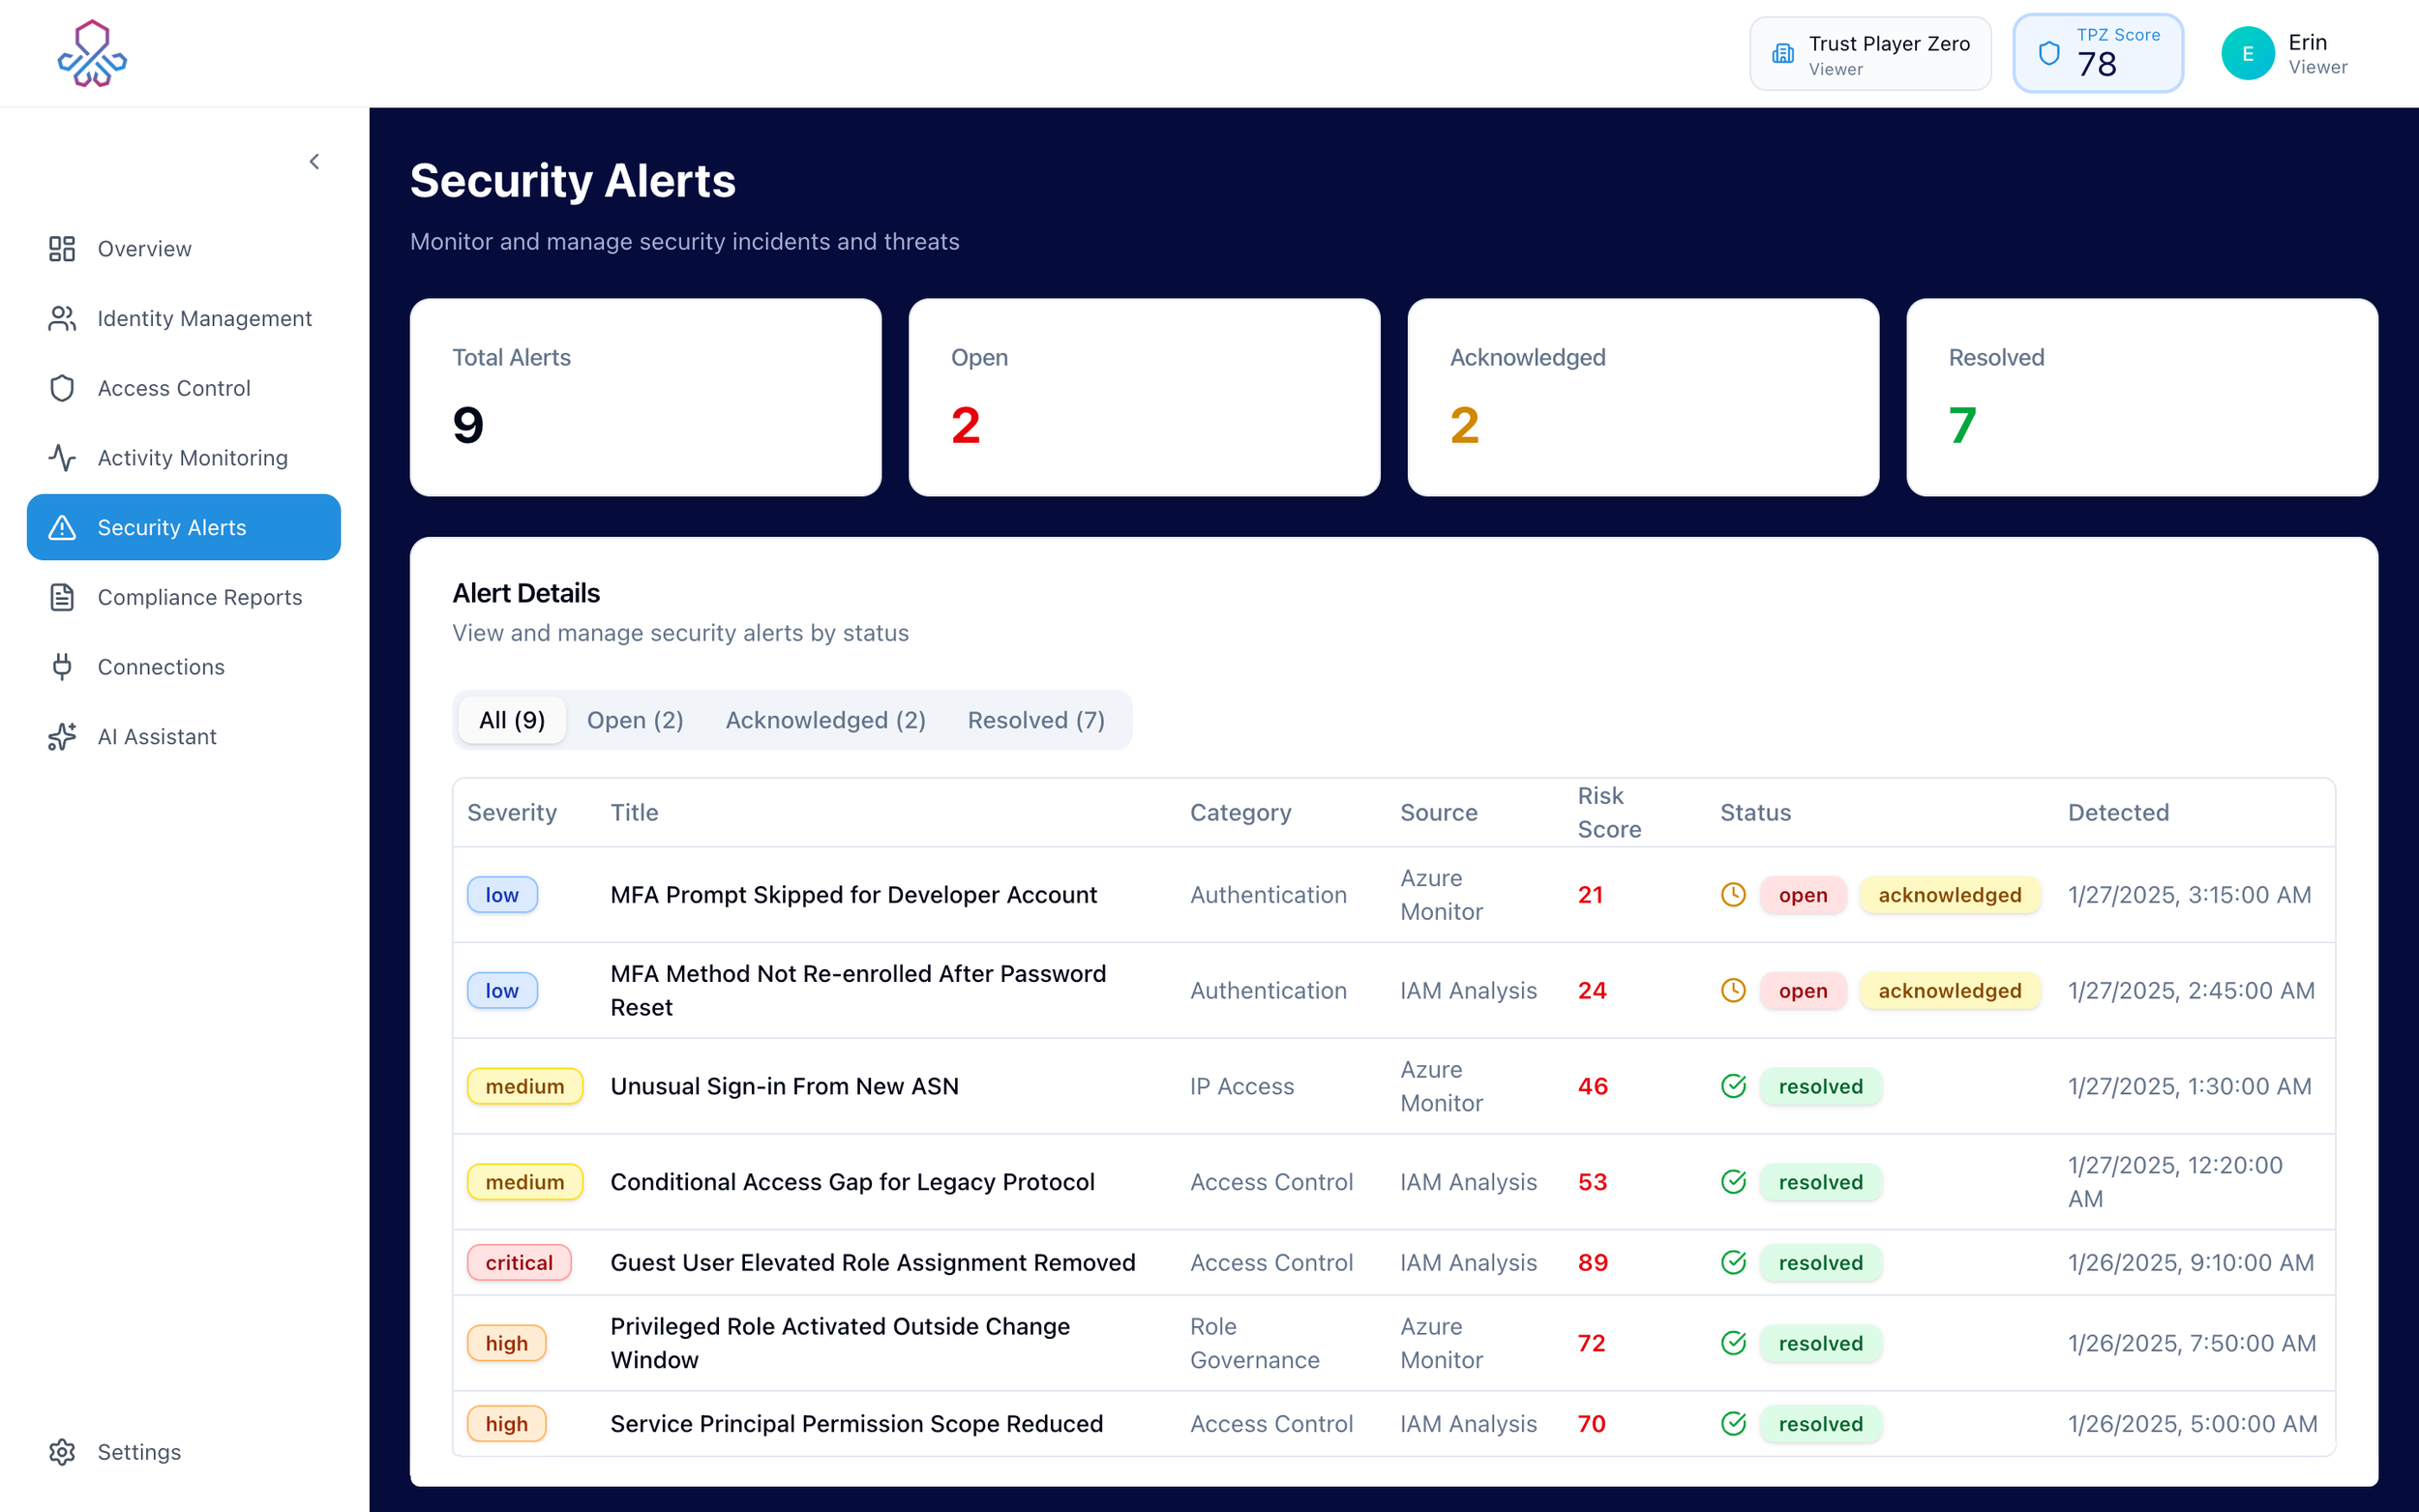
See risky users, unusual sign-ins, MFA registration gaps, and other supported signals that may need review.
Spot the issue
Review supported identity and access conditions that may require investigation.
Check the context
Examine account details, directory roles, MFA registration, recent activity, and related signals.
Decide what needs review
Use the available evidence to determine what requires further investigation or customer action.
STANDARD TPZ IDENTITY & ACCESS AUDIT V1
START WITH A CLEAR VIEW OF WHAT DESERVES REVIEW.
Organizations already manage access for employees, administrators, applications, and service accounts. AI agents introduce another challenge: software can increasingly initiate actions and operate across systems.
Security teams need to understand which identity is acting, what authority it has, who is accountable, and whether its actions produced the intended result.
TPZ's longer-term vision is to bring governed security decisions and verifiable outcomes across human, software, and AI identities.
DORMANT USERS
Accounts with extended periods of inactivity that may deserve review.
NEVER-SIGNED
IN USERS
Accounts with no observed sign-in activity in the available data.
PRIVILEGED USERS
Users with supported Microsoft Entra directory-role assignments.
PRIVILEGED USERS WITH MFA REGISTRATION GAPS
Privileged users without registered MFA methods
in the available Entra data.
STALE GUEST ACCOUNTS
Guest identities with
activity or age conditions that meet the audit’s defined review criteria.
IDENTITY RISK
SIGNALS
Supported Microsoft Identity Protection signals that may warrant investigation.
CURRENT
Read-only evidence, investigation, and supported identity and access context.
DESIGN PARTNER BETA
Move findings through review toward customer-authorized remediation, read-back verification, retained evidence, and governed recovery.
START WITH MICROSOFT ENTRA.
WHAT EXISTS TODAY
An inactive account, privileged role, or MFA registration gap may deserve investigation. The audit organizes supported evidence so your team can review the condition against its own policies and decide what happens next.
Coverage depends on configuration, permissions, licensing, and current product limits.DESIGN PARTNER BETA
From identifying a problem to proving what happened.
Finding an identity issue is the beginning of the work. Someone must decide what should change, approve the action, and confirm that the system reflects the intended result.
TPZ's Design Partner Beta is designed to validate this governed workflow, beginning with a customer-authorized Microsoft Entra disable action.
The customer remains responsible for approving the action. TPZ's Beta target is to execute the authorized change, read the resulting state back from Microsoft Entra, retain evidence, and support governed recovery.
FIND
See what needs attention.
Current
DECIDE
Review the evidence and determine the appropriate response.
Beta
FIX
Authorize and carry out the approved customer action.
Beta
VERIFY
Read the source system again, confirm the resulting state, and retain evidence.
Beta
You stay in control. Actions being validated in Beta require customer authorization.
DESIGN PARTNER BETA
HELP US PROVE THE NEXT STEP.
TPZ is working with a limited group of Design Partners to validate one customer-authorized Microsoft Entra workflow in real operating environments.
12 WEEKS
A focused Design Partner Beta with regular working sessions.
FREE TO PARTICIPATE
The program is designed around shared learning and validation.
ENTRA
A Microsoft Entra environment is required.
UP TO 5
A small cohort so we can work closely with each team.
WHAT WE’RE VALIDATING
The Beta target is to validate a customer-authorized Microsoft Entra disable action, read the resulting state back from Entra, retain evidence of what happened, support governed re-enable, and verify the restored state.
AUTHORIZE
DISABLE
READ BACK
RETAIN EVIDENCE
RECOVER
BUILT FOR THE PERSON ACCOUNTABLE FOR CYBERSECURITY IN A MICROSOFT-HEAVY ENVIRONMENT.
WHO IT’S FOR
TPZ is starting with Microsoft-heavy Financial Services and FinTech organizations where one person or a small team carries broad cybersecurity responsibility. The same people may be identifying identity and access risk, investigating what happened, coordinating decisions, and following through on what needs to change.
ACCOUNTABLE BUYER
Owns the security outcome and has authority over the relevant security or IT budget.
CHAMPION
Feels the identity and access pain directly and helps move the workflow forward inside the organization.
OPERATOR
Works hands-on with identity and access context and helps validate the workflow in practice.
One person may fill more than one of these roles.
UNDERSTAND WHAT TPZ CAN ACCESS.
SECURITY & DATA
TPZ connects to Microsoft Entra in read-only mode today. See how we handle permissions, data, access boundaries, and how those requirements change as the Design Partner Beta progresses.
As AI takes on more work, knowing who or what has authority becomes even more important.
FUTURE DIRECTION
Organizations already manage access for employees, administrators, applications, and service accounts. AI agents introduce another challenge: software can increasingly initiate actions and operate across systems.
Security teams need to understand which identity is acting, what authority it has, who is accountable, and whether its actions produced the intended result.
TPZ's longer-term vision is to bring governed security decisions and verifiable outcomes across human, software, and AI identities.
Want to see where TPZ is headed next?
Future direction. Not current product capability.DESIGN PARTNER BETA
READY TO WORK THROUGH A REAL IDENTITY AND ACCESS PROBLEM WITH US?
We’re working with a limited group of Design Partners to validate the workflow in real Microsoft Entra environments.